

Skip to content
Anexet
Product
Solutions
Features
Company
Services

Citizen Data Protection

Fully on-premises control over citizen records and controlled information, analysed inside your perimeter with no vendor access.

Schedule a Demo
Anexet console monitoring data activity inside a government agency

Why data protection is harder in government

Agencies process citizen identities, case and benefits files, controlled or classified material, and procurement records. That data moves constantly through email, messengers, the web, cloud storage, network shares, and removable media — often across mixed Windows, Linux, and macOS estates, multiple departments, and outside contractors.

Anexet runs entirely on-premises, so analysis stays inside your network and the vendor never touches your data. Where mandates demand isolated handling, an optional local AI model analyzes incidents on-site with no internet egress at all.

What keeps public-sector security teams up at night

  • Citizen-data exposure

    Personal records, case files, and identifiers leaking through email, chats, or cloud storage — by error or by design — with mandatory breach notification on the line.

  • Controlled & classified information

    Sensitive and controlled material that must stay inside the perimeter being copied to personal accounts, USB drives, or unsanctioned channels.

  • Insider risk inside the perimeter

    Cleared staff and contractors with legitimate access mishandling data — the hardest threat to catch with network defenses alone.

How Anexet protects public-sector data

One on-premises platform — data-leak prevention, employee activity monitoring, and IT inventory — built so sensitive citizen and controlled data is analyzed and contained inside your own perimeter.

  • Analysis stays inside your perimeter

    Anexet deploys fully on-premises: databases, the console, and processing all live inside your network, and the vendor has no access to your data. Built for the isolated, tightly segmented environments that government runs on.

  • Local AI with zero internet egress

    An optional on-premises AI model summarizes incidents, filters false positives, and analyzes evidence locally — nothing is sent to the cloud or any external service, so even air-gapped analysis stays self-contained.

  • Catch every channel through which data can leave

    Email, 25+ messengers and team chats, web uploads and search, cloud storage, network shares, printing, the clipboard, USB and removable devices, and SIP/VoIP are intercepted on the endpoint across Windows, Linux, and macOS.

  • Block sensitive data by its content, not just its path

    Security rules and alerts stop policy-violating transfers, while content-aware blocking based on digital fingerprints, hash banks, and confidentiality labels keeps protected documents inside the perimeter even when renamed. OCR reads scans, including seals and stamps.

  • Investigate with court-grade evidence

    User-behavior analysis scores risky activity and identifies insider risks, and full incident investigations build a complete, attributable trail to reconstruct events and support disciplinary, administrative, or legal proceedings.

  • Fit your governance model

    Role-based access control scopes who sees what across the policy and risk modules, SIEM integration feeds events into your security operations, and on-screen watermarks deter and trace leaks of classified material.

Supports your compliance program

Anexet helps your organization support the data-protection and information-handling requirements that apply to public bodies, including:

  • NIST 800-171
  • GDPR
  • Regional public-sector data-protection requirements

Anexet is a compliance-support tool. It is not a certification and does not replace your own legal or audit assessment.

A closer look at the consoles your security and IT teams use to monitor activity, enforce policy, and investigate incidents — all inside your own perimeter.

  • Anexet console reviewing intercepted email, messenger, web, and cloud communications

    Review intercepted communications across email, messengers, web, and cloud.

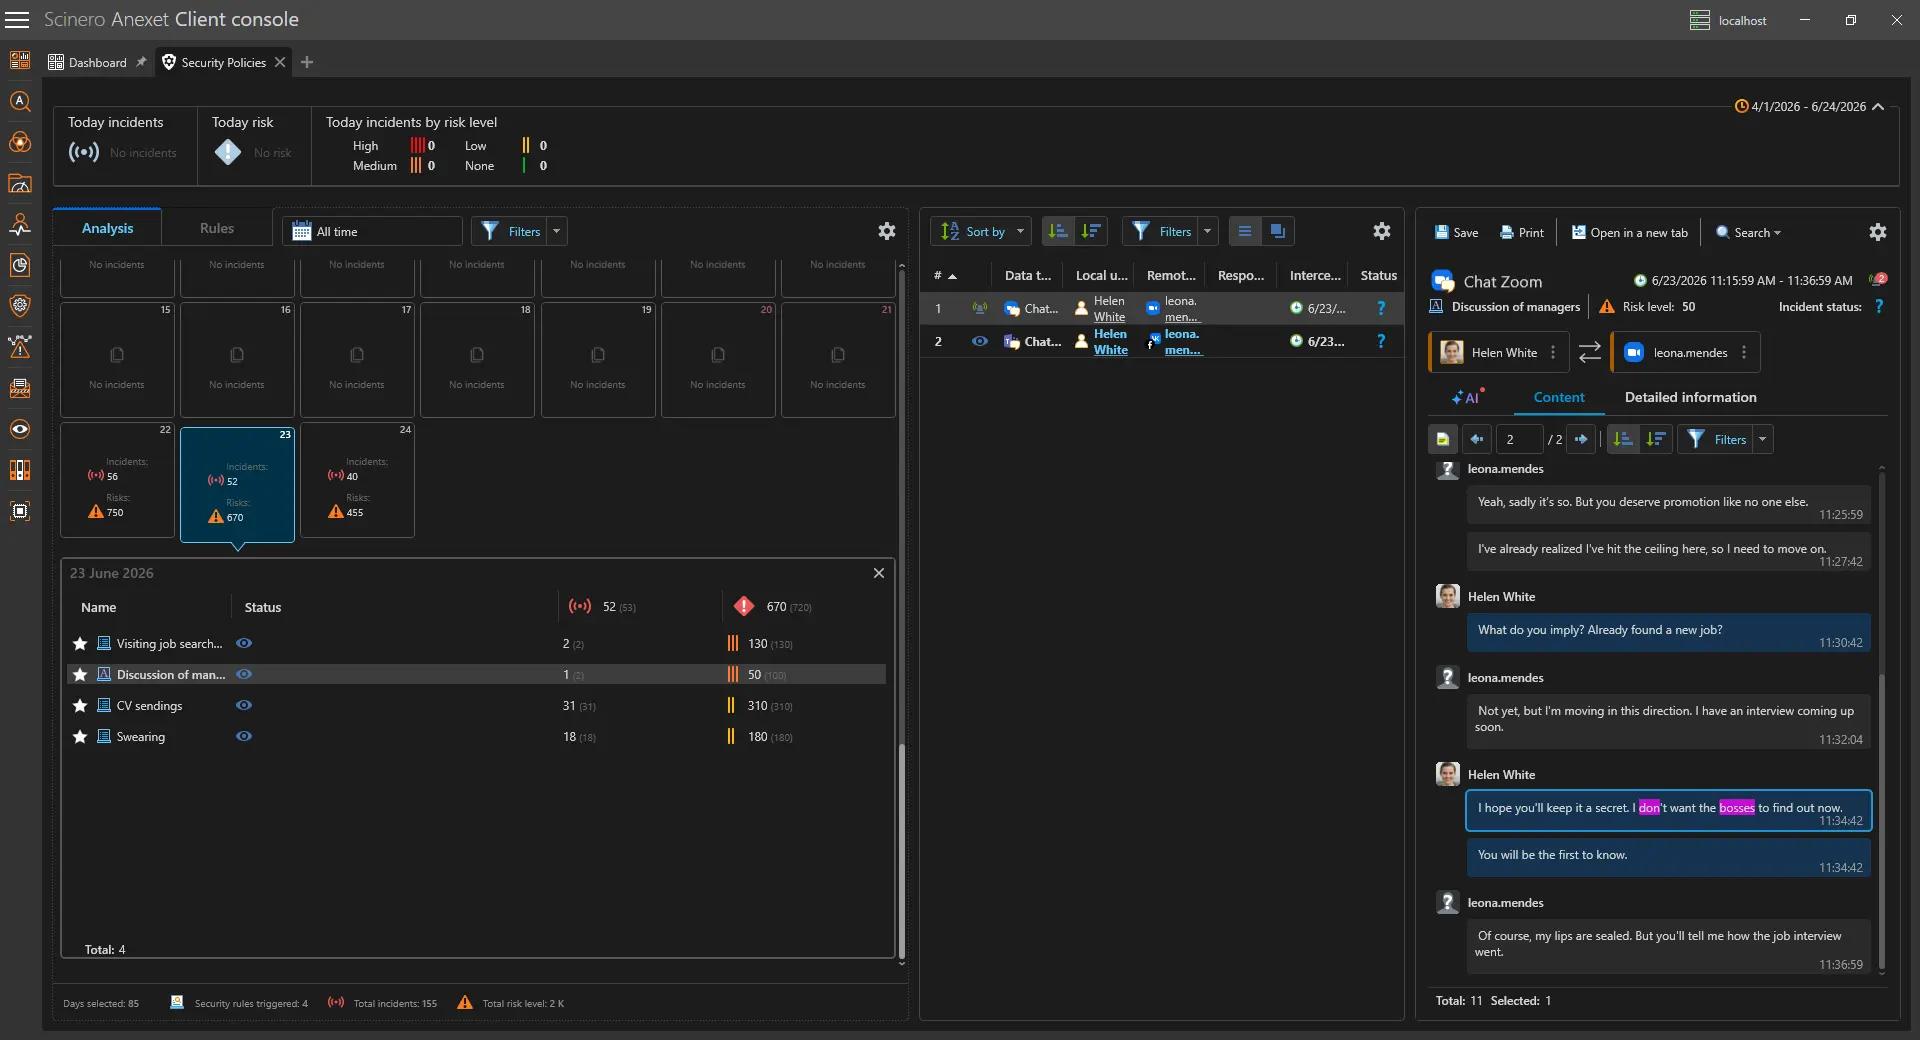
  • Anexet console configuring security policies and automatic risk-based blocking

    Define security policies and risk rules — and block violations automatically.

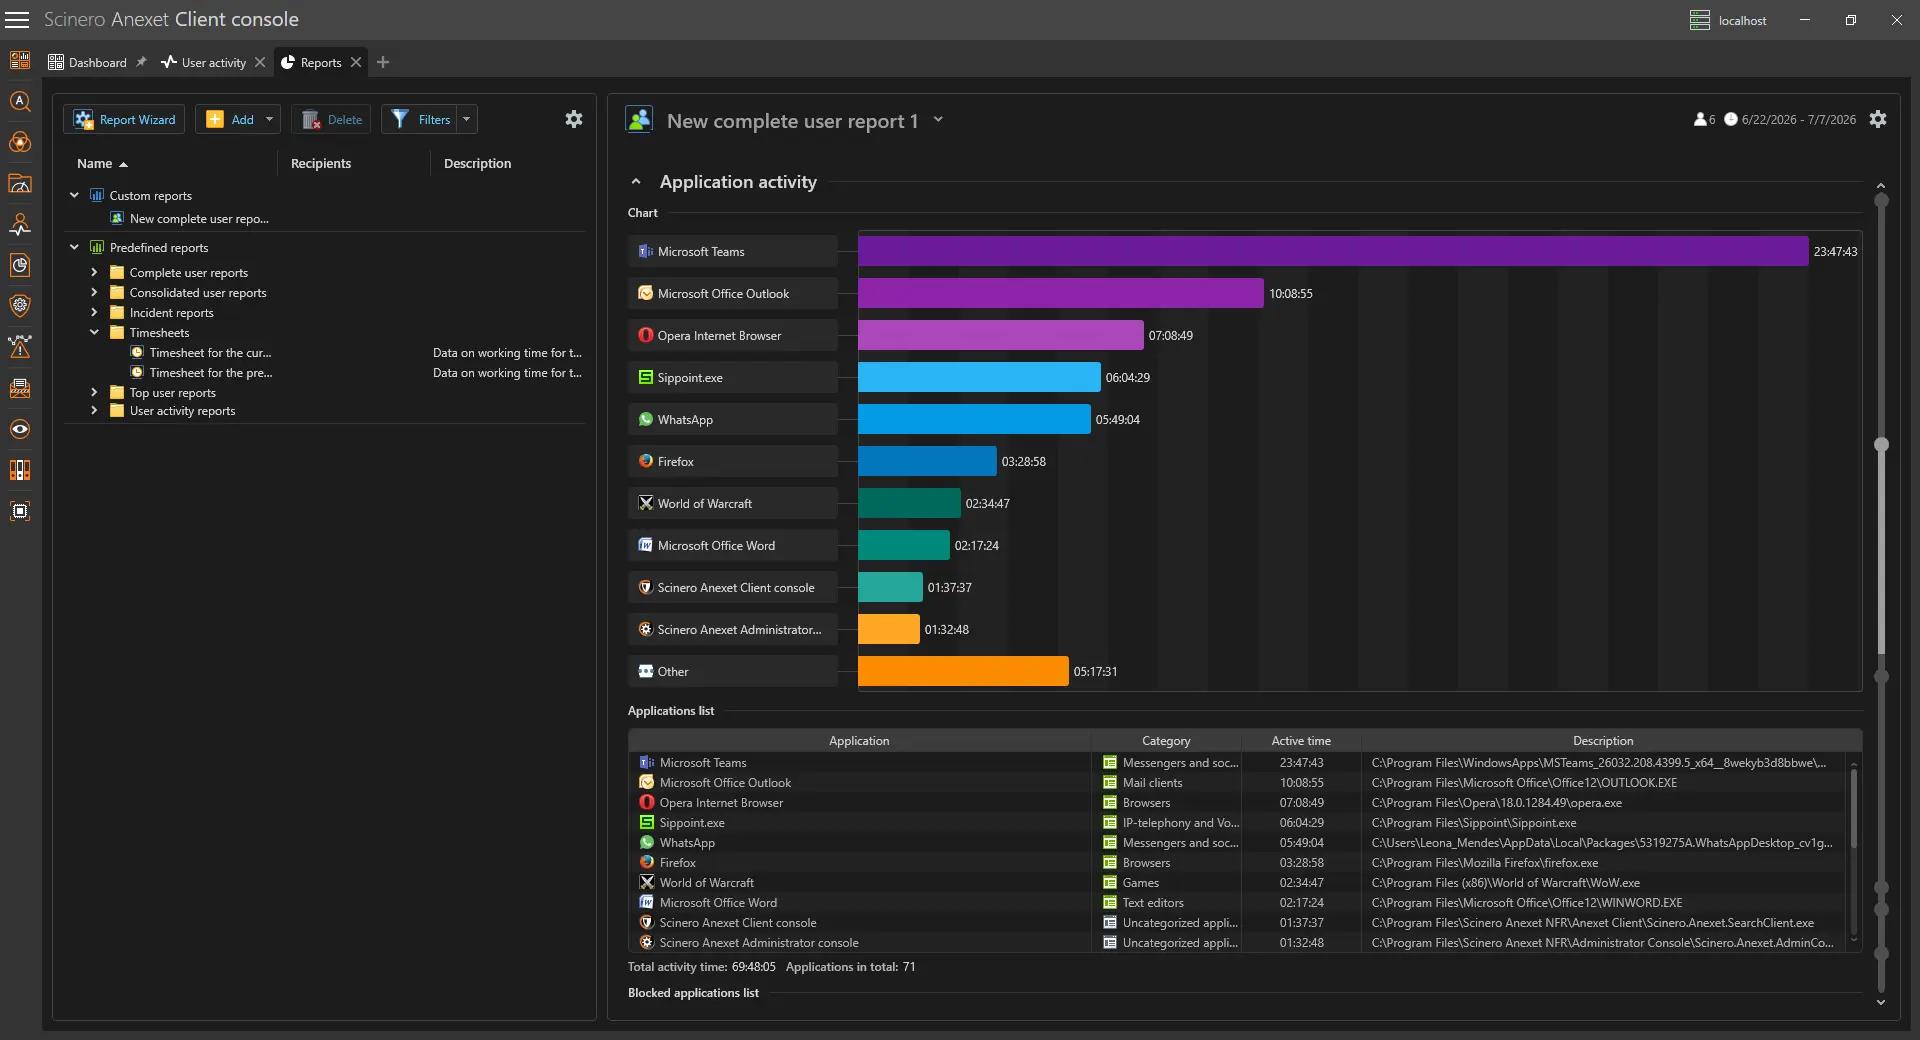
  • Anexet console showing employee activity and productivity across applications and websites

    Monitor employee activity and productivity across applications and sites.

  • Anexet console generating incident reports and dashboards for investigations and audits

    Generate incident reports and dashboards for investigations and audits.

Capabilities public-sector teams rely on

This solution draws on a few Anexet capabilities in particular:

From first conversation to full control

Setting Anexet up inside your perimeter is a short, guided path your team controls end to end.

Tell us about your environment, isolation requirements, channels, and the regulations you are subject to.

1

Deploy fully on-premises inside your network and roll out cross-platform agents to the endpoints you choose.

2

Turn on policies for the citizen data, controlled information, and channels that matter most.

3

Monitor activity, get alerted, investigate incidents with local AI, and tune rules as you scale.

4

Tell us about your environment, isolation requirements, channels, and the regulations you are subject to.

1

Deploy fully on-premises inside your network and roll out cross-platform agents to the endpoints you choose.

2

Turn on policies for the citizen data, controlled information, and channels that matter most.

3

Monitor activity, get alerted, investigate incidents with local AI, and tune rules as you scale.

4

Arrow

Public-sector protection by plan

StandardCore employee activity monitoring.
Network traffic interception
USB control
Printer monitoring
Messenger interception
Browser interception
and 4 more
Most popular
AdvancedAdds DLP and deeper visibility.
Standard plan included
DLP features
Network share monitoring
Keylogger
Webcam pictures
and 4 more
All-in-one
PremiumAll-in-one solution.
Standard + Advanced plans included
Advanced search (digital fingerprints, hash search)
File system monitoring
User relationship analysis
Risk analysis
and 6 more

Public Sector FAQ

Common questions about deploying Anexet in government bodies and public agencies.

How does Anexet protect citizen and controlled data?

Anexet monitors how sensitive information — citizen records, case files, controlled and classified material — moves across email, messengers, web, cloud, network shares, and devices, and can block policy-breaking transfers on digital fingerprints, hashes, and confidentiality labels before data leaves the endpoint.

Yes. Anexet is deployed fully on-premises inside your own perimeter, the vendor has no access to your data, and the optional local AI model analyzes incidents on-site with no internet egress — so it suits isolated and tightly segmented government networks.

Everything stays inside your network: databases, console, and analysis all run on-premises, and the vendor never sees your data. Role-based access control scopes which of your own staff can view policy and risk data.

Anexet helps your organization support requirements such as NIST 800-171, GDPR, and regional public-sector data-protection requirements by controlling data movement, logging access and file operations, and producing incident reports. Anexet itself is not a certification and does not replace your legal or audit assessment.

Pricing is available on request. Tell us your environment and the number of endpoints, and we'll recommend the right plan — Standard, Advanced, or Premium.

Three professionals collaborating and looking at a tablet in a meeting

Protect citizen and controlled data with Anexet

Tell us about your agency, environment, and isolation requirements — we'll recommend the right plan and walk you through a tailored demo.

I accept that my personal data can be processed in accordance with the Privacy Policy